Create Free Account

Contractor Management Software for Compliance & Legal

When You’re Asked. Show the File. Not the Memory.

Every certification, every sign-off, and every check on one record, with a name and a date against it. Somebody asks what was verified, and you show them.

  • General Counsel
  • Company Secretary
  • Head of Legal
  • Head of Compliance
  • Compliance Manager
  • Chief Risk Officer
  • Privacy Officer
Two people at a small meeting room table, one showing the other a document on a tablet during a vendor security review, business dress, no boardroom or courtroom in the frame ISO 27001 since 2019, hosted in Australia, every check dated

ComplyFlow for Compliance & Legal.

Contractor compliance software built to be checked, not taken on faith. Every certification, sign-in, and sign-off sits on one exportable record with a name and a date against it, so the evidence a vendor review, an audit, or a subpoena asks for already exists before anyone asks for it.

  • The certificate and the hosting answer are already written down. ISO 27001 since 2019, AWS hosting in Australia, and the policy behind both, ready before your questionnaire is sent.
  • Your identity provider decides who gets in, and who gets removed. Single sign-on through Microsoft or Okta, so a leaver’s access ends when your directory says so, not when someone remembers.
  • Every check carries a name and a date, filtered and exported. By site, contractor, or date range, in the form a regulator, an auditor, or a subpoena actually asked for.
  • Nothing about the record is a black box. The API is open, and AI reads the record but cannot write to it. Where a subprocessor question is not answered on this page, we answer it directly in your review, not with a guess.
ISO 27001 certified since 2019, hosted on AWS in Australia, encrypted at rest and in transit.
Microsoft and Okta single sign-on, so a leaver’s access ends when your directory says so.
The first contractor compliance platform we can find with its own MCP server.

ComplyFlow Is Already Trusted by Your Peers.

Legal, risk, and compliance teams in government, transport, property, and heavy industry have already cleared ComplyFlow on the same evidence you are about to ask for.

Your Week

The Six Moments That Land on a Compliance & Legal Desk.

Every one of these is evidence demanded of you, not a feature you are shopping for. Each shown twice: now, and on one record.

  1. Monday

    A new vendor lands for security sign-off.

    Today

    A standard questionnaire goes out, and the certificate that comes back sits unread in an inbox until next year.

    With ComplyFlow

    Certification status, data residency, subprocessors, and renewal dates sit on one record.

  2. Tuesday

    A new project needs a privacy assessment before it starts.

    Today

    You chase the project owner for what data moves where, and sign off with caveats nobody tracks.

    With ComplyFlow

    The assessment sits against the project and the supplier record it touches, so the next reviewer starts from what is known.

  3. Wednesday

    A contractor disputes a rejected insurance certificate.

    Today

    Someone digs through email and a shared drive for when it was checked and against what rule, and the dispute outlasts the actual gap in cover.

    With ComplyFlow

    The check, the date, the reviewer, and the rule applied are on the record.

  4. Thursday

    A regulator’s notice asks what was done, and when.

    Today

    A scramble across four systems and a folder to reconstruct a timeline before the response is due.

    With ComplyFlow

    Filter by date and site, and export what was verified, in a form a regulator can rely on.

  5. Friday

    The modern slavery statement needs board sign-off next week.

    Today

    Procurement, risk, and legal each hold a slice of the supply-chain picture, and one supportable statement is a cross-team chase against a deadline.

    With ComplyFlow

    One verified record serves all three functions, not a chase against the clock.

  6. Any day, no warning

    A subpoena or a discovery notice asks for records going back years.

    Today

    A search across whichever system was in use at the time, hoping nothing was deleted or never digitised.

    With ComplyFlow

    Every induction, licence check, permit, and sign-in has a name and a time against it, exportable for the dates asked for.

This describes the job as the research behind this page found it, not a measured saving in your business. What changes is whether the record exists before anyone asks for it.

What You Open Most

The Four Things Compliance & Legal Opens Most.

Not a feature list. The four screens that carry the jobs you cannot afford to let slip.

Every Vendor, Measured Against Your Own Checklist.

Certification, hosting, subprocessors, and renewal dates for every vendor sit on one record, read against the questions your security review actually asks. A new vendor lands, and the answer does not wait in an inbox for a year.

  • Certification, residency, and subprocessors, on one record
  • Renewal dates chased before they lapse
  • Filtered by vendor, contractor, or date

AI Reads the Assessment Before You Do.

Upload a privacy assessment, a contract, or a supplier statement and AI reads it against the criteria you set, section by section. It comes back with what it found and what is missing. You review the gaps and make the call.

  • Section-by-section read against your own criteria
  • The reasons shown, so you can disagree with it
  • A person signs off; the AI never does

What Every Token Outside ComplyFlow May Read.

The same model your own security review checks. A personal token carries read scopes only, expires within a year, and inherits the permissions of the person who made it. Nothing outside the product can write to the record.

  • Read scopes only, per module
  • Expiry from 7 days to one year
  • Revoked on confirmation

The Export a Regulator or a Subpoena Actually Asks For.

Filter by site, contractor, or date range, and produce every check, with a name and a time against it, in the form the request named. Not a screenshot. Not a reconstruction.

A compliance manager at a desk exporting a filtered contractor compliance record on a laptop, a printed regulator notice beside the keyboard, a meeting room visible through glass behind them

How It Helps

Digitised. Automated. AI-Reviewed. Every Job on Your List.

Three things make ComplyFlow different, and every job on this list draws on all three.

  • 01

    The Whole Lifecycle, on One Record.

    Vendor check to subpoena response: certification, contractor, and supplier evidence on one record. Nothing sits in an inbox for someone to find later.

  • 02

    Your Checklist, Digitised & Automated.

    The vendor questionnaire, the privacy assessment, and the renewal reminder become one system that checks and chases without you.

  • 03

    AI That Does the Reading.

    Contracts, assessments, and statements read against your standard in seconds, with the reasons shown. You still make the call.

What you do Digitise Automate AI
Review a new vendor The questionnaire and the certificate land on one record instead of an inbox. Renewal dates and subprocessor changes are flagged before they lapse. The certificate read against your requirements, with the gaps listed.
Run a privacy assessment The assessment sits against the project and the supplier record it touches. It cannot be signed off while a required section is missing. Read section by section, with a grade and the reasons.
Check a contractor’s insurance The certificate, the date, and the rule applied sit on the contractor’s record. A lapsed certificate is flagged the day it happens, not the day it is disputed. Read against your requirement set as it is uploaded.
Answer a regulator’s notice Every check sits on one searchable record instead of four systems and a folder. Filtered exports run by site and date, not rebuilt by hand. Ask your assistant what was verified for a site or a contractor, through MCP.
Prepare the modern slavery statement One verified contractor and supplier record serves procurement, risk, and legal. Coverage is measured against the whole panel, not a manual sample. Ask which suppliers are missing a current statement.
Respond to a subpoena or discovery notice Every induction, licence check, permit, and sign-in has a name and a time against it. Exported for the date range asked for, not searched for by hand. Ask what a Worker or contractor was checked against, and when.
Track a subprocessor change Every vendor’s subprocessor list sits on the same record as its certification. A change is flagged the day it is notified, not the day someone asks. Ask which vendors have changed a subprocessor this quarter.
Report to the board One searchable record instead of a chase across four teams. Live status straight into Power BI. Ask in plain English through Claude, Claude Code, or GitHub Copilot; the answer comes from the record.

The Numbers You Run On

The KPIs Compliance & Legal Reports, and Where Each One Comes From.

What a board, an auditor, or a regulator asks you for, and the record it is read from.

Reads from names the ComplyFlow record each measure is read from. The targets are yours.

  1. Audit finding closure rate

    The share of findings closed by their due date

    Reads fromCorrective actions, owned and dated

  2. Evidence production time

    How long a regulator or subpoena request takes to answer in full

    Reads fromRequests, logged from ask to export

  3. Vendor review cycle time

    New supplier to completed certification and subprocessor check

    Reads fromThe vendor record, dated at each step

  4. Breach notification timeliness

    Whether a notifiable breach was reported as soon as practicable

    Reads fromThe incident record, timestamped

  5. Modern slavery coverage

    The share of suppliers with a current, verified record

    Reads fromThe supplier record, live, by tier

  6. Contractor panel currency

    The share of contractors whose checks are in date today

    Reads fromThe prequalification record, live, by site

Book a Demo

Bring Your Week. We Will Show It Running for Compliance & Legal.

A 30-minute call with someone who has set ComplyFlow up for people in your role: your sites, your contractors, and the questions you get asked, in the product rather than on slides.

  • The week above walked through on a live account, not a demo dataset
  • The report or export you are asked for most, produced in front of you
  • A straight answer on rollout for your number of sites and contractors
Talk to Us Instead

No slides, no hard sell. A working session on your own set-up.

Book Your Demo

Thirty minutes, on your own requirements.

Book Demo

The form loads from HubSpot. If it does not appear, the button takes you to the demo request page.

Fits Your Governance Stack

Slots Into the Systems You Already Run.

Read it left to right: where your governance work already runs, the one record that checks it, and where your evidence goes.

Where your governance work already runs

GRC platformsServiceNow GRC, OneTrust, Diligent, and LogicGate, where your risk and compliance register already lives
Contract lifecycle managementDocuSign CLM and Icertis, where supplier contracts and audit-rights clauses sit
Legal matter & document managementiManage, NetDocuments, and Xakia, where a matter or a board paper is drafted
Records managementOpenText Content Manager and Objective, where a subpoena is usually answered from
Microsoft & Okta sign-onYour people log in the way they already do SSO
PrequalificationWorkforce ComplianceTraining & InductionSite AccessVisitor Sign-InSite DocumentsDigital PermitsInspections & AuditsPlant & EquipmentIncident ManagementRisk Management ComplyFlow. One Record.

Where your evidence goes

Power BI dashboardsCertification, retention, and audit status, by supplier and by site, live
The board and audit packWhat was verified, by whom, and when, without a week of assembling it
The regulator or subpoena exportEvery check, filtered by site and date, in the form the request asked for
AI assistants via MCPAsk Claude, Claude Code, or GitHub Copilot which suppliers or contractors are short on a requirement MCP
Legislation MonitorReads every WHS Act, Regulation, and Code of Practice across Australia; it does not read procurement rules or the Modern Slavery Act

Sign-on and the Legislation Monitor are ComplyFlow’s own. Everything else connects through the open API and MCP, so if a system in your stack has an API, it belongs on this drawing.

The Care & Diligence Duty

The Duty That Attaches to General Counsel and the Company Secretary.

Section 180(1) asks you to exercise the care and diligence a reasonable person would, in your circumstances and your office. It is not written for directors alone.

A director or other officer of a corporation must exercise their powers and discharge their duties with the degree of care and diligence that a reasonable person would exercise if they: (a) were a director or officer of a corporation in the corporation’s circumstances; and (b) occupied the office held by, and had the same responsibilities within the corporation as, the director or officer.
Corporations Act 2001 (Cth), section 180(1), legislation.gov.au

The courts have already rejected splitting a dual role to escape it. In Shafron v ASIC, the High Court held that James Hardie’s general counsel and company secretary could not treat his two roles as separable to avoid section 180, calling them indivisible. He was disqualified from managing corporations for seven years and fined AU$50,000.

Shafron v ASIC [2012] HCA 18.

What you can hand over

  • The certification recordWhen ISO 27001 was certified, its scope, and when it was last reviewed.
  • The vendor security fileEvery supplier’s certification status, data residency, subprocessors, and renewal date, on one record.
  • The privacy assessmentWhat data a project moves, where it goes, and what conditions the sign-off carried.
  • The contractor check trailWhen each insurance certificate or licence was checked, against what rule, and by whom.
  • The regulator response packEvery verified check, filtered by date and site, exported in the form the request asked for.
  • The modern slavery evidenceThe supplier and contractor record the statement draws on, verified rather than sampled.

Nothing here is legal advice, and ComplyFlow does not discharge any duty. What changes is whether the evidence exists, and whether it can be produced on the day someone asks for it.

The Numbers

What the Regulator Recorded, and What We Can Show You.

Public figures from the regulator, and the one certification date a vendor review checks first. Never a parked figure, never a competitor’s research.

Free From ComplyFlow. No Account Needed.

Know When a WHS Rule Changes, Before It Reaches Your Risk Register.

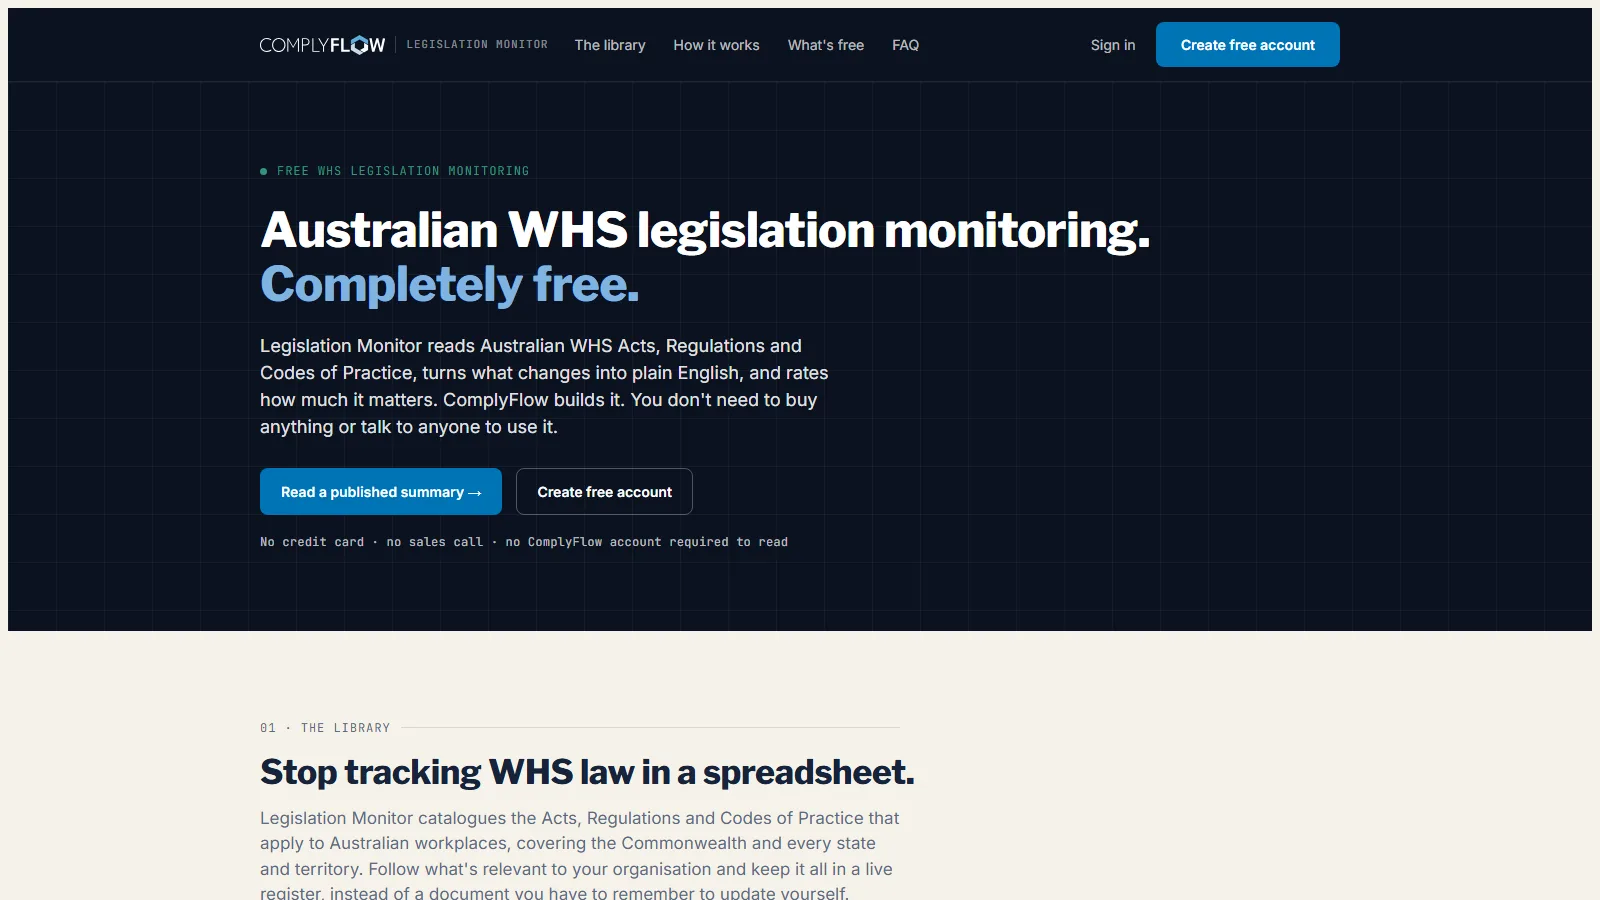
Free for anyone. It reads every Australian WHS Act, Regulation, and Code of Practice, not procurement rules and not the Modern Slavery Act, turns each change into plain English, and rates how much it matters.

Sign Up Free No credit card. No sales call.

monitor.complyflow.com
The Legislation Monitor home page: Australian WHS legislation monitoring, completely free
  • 390 instruments across all nine Australian jurisdictions
  • A plain-English summary and a severity rating for every change
  • AI reads the change, a person checks it, a Tuesday digest tells you

Why ComplyFlow

Why ComplyFlow, Not a GRC Platform or a Shared Drive.

A GRC platform holds the risk register once it is built. A shared drive holds the document. Neither one verifies what it claims, or keeps a name and a date against the check.

GRC platformsHolds the risk register once it is built; does not check a contractor’s insuranceContract & matter managementHolds the document; does not verify what it claimsSpreadsheets & shared drivesFree, and relies on someone remembering to update it ComplyFlowOne record, your standard
Vendor certification, hosting, and subprocessors on one record PartlyNot thereNot there Certification, residency, and subprocessors, dated and renewed
Contractor insurance and licence checks, dated and ruled Not thereNot thereNot there Every check with a name, a date, and the rule applied
Privacy assessments tied to the project and the supplier PartlyPartlyNot there The assessment sits against both, not filed alone
A regulator or subpoena export filtered by site and date Not thereNot thereNot there Filtered and exported in the form the request asked for
Modern slavery coverage measured across the whole panel PartlyNot thereNot there Coverage measured against the verified record, not a sample
AI that reads a contract or assessment against your criteria Not therePartlyNot there Read section by section; a person signs off
Read-only tokens and AI access, scoped and expiring Not thereNot thereNot there cf_pat_ tokens carry read scopes only; MCP cannot write
ISO 27001 certified, hosted in Australia Built inNot thereNot there Certified since 2019; all data within Australia

This compares kinds of product, by how they are sold, not named vendors. Named comparisons, with dates and sources, live on the comparison pages.

Getting Started

We Set It Up With You. We Stay With You.

You are not handed a login and left to it. Our onboarding team answers your review, builds your record with you, and stays on hand once it is live.

  • Mitch Bourne, ComplyFlow
  • Jessica Morgan, ComplyFlow
  • Sam Bourne, ComplyFlow
  • Phil Wallach, ComplyFlow
  • John McCann, ComplyFlow
  1. 1 We Map Your Checklist

    Every certification, policy, and document your security or privacy review needs, and what you want on the record from day one.

  2. 2 We Answer Your Vendor Questionnaire

    The ISO 27001 certificate, hosting and subprocessor detail, and written answers to your review, before you sign anything.

  3. 3 We Set Up Your Record

    Contractor and supplier requirements, retention, and export formats, built with you rather than guessed at.

  4. 4 You Go Live, We Stay Close

    Training for your team, written guides for everyone, and a support team that picks up the phone.

  • ISO 27001 certified ISO 27001Certified 2019
  • AWS Qualified Software Certified 2023
  • GDPR, General Data Protection Regulation Compliant 2020
  • Microsoft Okta Single sign-on

Security & Data

Certified, Audited & Hosted in Australia.

Your compliance record is the evidence you rely on when somebody asks, so where it lives and who can reach it matters. ComplyFlow is ISO 27001 certified, runs on AWS in Australia, and your people sign in with the accounts they already have.

Questions

Questions Compliance & Legal Asks Before They Book a Demo.

Are you ISO 27001 certified, and can we see the certificate and its scope?

Yes. ComplyFlow has held ISO/IEC 27001 certification since 2019, and AWS Qualified Software status since 2023. Ask for the certificate as part of your review and we will provide it, with its issue date, its scope, and its certifying body.

Where is our data hosted, and does it leave Australia, including support?

All data is hosted in Australian data centres, on AWS as Qualified Software, and encrypted at rest and in transit. Whether a support interaction ever needs data to leave Australia is a fair question to put to us directly; it is not something this page can confirm either way, and we would rather say that than guess.

What is your retention policy, and can we set our own period per record?

Retention sits in the Information Security Policy, which we send as part of a vendor review. We are not going to put a figure on this page that we have not confirmed against your own requirement; ask for the policy and we will answer it plainly in the review.

Who are your subprocessors, and do we get notice before you add one?

We have not published a subprocessor list on this page, and none is named in the security documentation this page draws from. It is a fair question, and one we would rather answer straight in your review than leave unaddressed here; ask for it and we will confirm the current list and how a change is notified.

Can every check be exported with a name, a time, and what was verified, in a form that holds up to an auditor or a court?

Yes. Every approval, check, and sign-in carries a name and a time, filtered by site, contractor, or date range, and exported as PDF. Whether that satisfies a particular court’s evidentiary rules is a question for your own counsel; what ComplyFlow gives you is the record itself, not a judgement on it.

Do you support single sign-on, and what happens to access on offboarding?

Yes. Microsoft and Okta, through OAuth 2.0, with your own MFA and conditional access policies applied. Access follows your identity provider, so when your directory removes someone, their access here ends with it rather than needing a separate step.

What happens to our data if ComplyFlow fails or is acquired?

We have not found a published data escrow or exit guarantee to point you to. Every record is exportable by you, on demand, in the PDF and CSV forms your audits already use; if a specific contractual guarantee is a condition for you, raise it in the review and we will answer against your requirement rather than a generic promise here.

Where AI reviews a document, what is the audit trail behind that call, and is a human decision always shown sitting on top of it?

Every AI read is kept with the document it graded, showing what it found and why. A named person approves, rejects, or closes it; the AI does not decide on its own, and the record shows both the AI’s read and the person’s decision sitting on top of it.

See the Evidence Against Your Own Checklist.

Book a 30-minute demo. Bring your vendor security questionnaire and we will answer it against the certificate, the record, and your own contractors and suppliers. No slides, no hard sell.

  • ISO 27001
  • Hosted on AWS
  • Microsoft & Okta SSO
  • API & MCP
  • Data in Australia

Compliance you can prove, instantly.